The Supervisor New York Already Built
Two essays this month proposed embedded evaluators for frontier AI and reached for bank supervision as the model. A state financial regulator has already been handed the job.
Read more
Regulator-Grade Judgment. Operator-Level Execution.
Serving: Regulated financial institutions and federal, state, and local agencies.
Critical during: Examinations, finding remediation, chartering, M&A, modernization, and AI adoption.
Examination readiness, supervisory remediation, and AI governance for institutions that answer to the OCC, FDIC, Federal Reserve, and NYSDFS.
Technology, cyber, and AI governance for agencies, available through HUBZone and SDVOSB sole source, set-aside, and subcontracting pathways.
Eight practice areas, organized by the outcome each one delivers.
Leadership can direct, fund, and hold the technology function accountable with confidence.
Risk is measured, prioritized, and reduced against the threats that actually matter to the mission.
Artificial intelligence is adopted with defensible controls, documented decisions, and clear ownership.
Shared responsibility is understood, configured, monitored, and evidenced.
Disruption is anticipated and absorbed rather than discovered in production.
Examinations, audits, and assessments produce fewer surprises and shorter remediation cycles.
Boards and executives receive technology risk in language they can act on.
Buying decisions are grounded in risk, contract terms, and lifecycle cost rather than vendor narrative.
Applying a regulator's judgment before regulators do.
Plenty of advisors have one of these three backgrounds. Some have two. The order is what makes the combination credible.
West Point graduate and commissioned Army officer in air and missile defense. Managed a $100 million defense technology program while managing fifty soldiers.
IT and cybersecurity examiner with the New York State Department of Financial Services, then Senior IT and Cybersecurity Examiner with the Office of the Comptroller of the Currency.
Founder and Chief Executive of Black Knight Risk Management, putting command judgment and regulatory authority to work for the institutions being examined rather than against them.
Clarity on risk posture and supervisory priorities.
Align strategy and accountability during critical inflection points.
Supervisory lens across IT, cyber, and operational risk.
Surface issues early, before escalation, enforcement, or costly remediation.
Two structured programs that build executive judgment before an examiner or an adversary tests it.
A structured executive workshop program covering how supervisory conclusions are reached, what evidence holds up under examination, and how leadership should govern technology risk between exam cycles.
Built for boards, executive teams, and risk committees that want to understand the examination process as participants rather than subjects.
Inquire about a sessionA facilitated cybersecurity tabletop exercise built on a realistic third-party breach scenario. It is designed to teach executives how to fight back, not how to take notes.
Participants take one of four executive roles and work through five escalating phases: regulatory notification clocks, a ransom demand, continuity decisions, and the governance that should have been in place beforehand. Every participant holds a role, and every role answers for a decision.
The same practice, written for the person who has to justify the conversation to someone else. One-pagers for financial institutions, universities, technology providers, and consulting firms, plus capability statements for contracting officers. Each is a single page, in PDF.
Announcements from the firm, and commentary on technology governance, supervisory expectations, and the decisions executives face before an examiner arrives.
Two essays this month proposed embedded evaluators for frontier AI and reached for bank supervision as the model. A state financial regulator has already been handed the job.
Read moreTwenty-three Baruch College students took four executive roles and worked a third-party ransomware breach against the clock. Satisfaction at the close was measured at 100 percent.
Read moreShorter notes on technology risk, supervisory developments, and governance practice, published regularly.
Follow on LinkedInPartners are engaged based on scope, supervisory context, and client needs. Black Knight remains the primary point of accountability and coordination.
Black Knight does not resell hardware or software and does not accept vendor commissions that would compromise the objectivity of its advice. Referral relationships, where they exist, are disclosed.
Veteran-led cybersecurity advisory firm delivering vCISO leadership and
regulator-aligned cyber program execution for highly regulated institutions.
Engaged within Black Knight initiatives when embedded leadership or exam-facing
execution depth is required.
Specialized ERP access-control and segregation of duties advisory expertise
focused on granular application-layer risk, role remediation, and SaaS control
sustainability.
Engaged within broader Black Knight regulatory engagements when ERP-specific
precision is required.
A Regulator's Perspective
Founded by a former Senior IT and Cybersecurity Examiner with the Office of the Comptroller of the Currency, Black Knight Risk Management advises regulated institutions and government agencies on designing, executing, and defending risk programs that hold up under scrutiny.
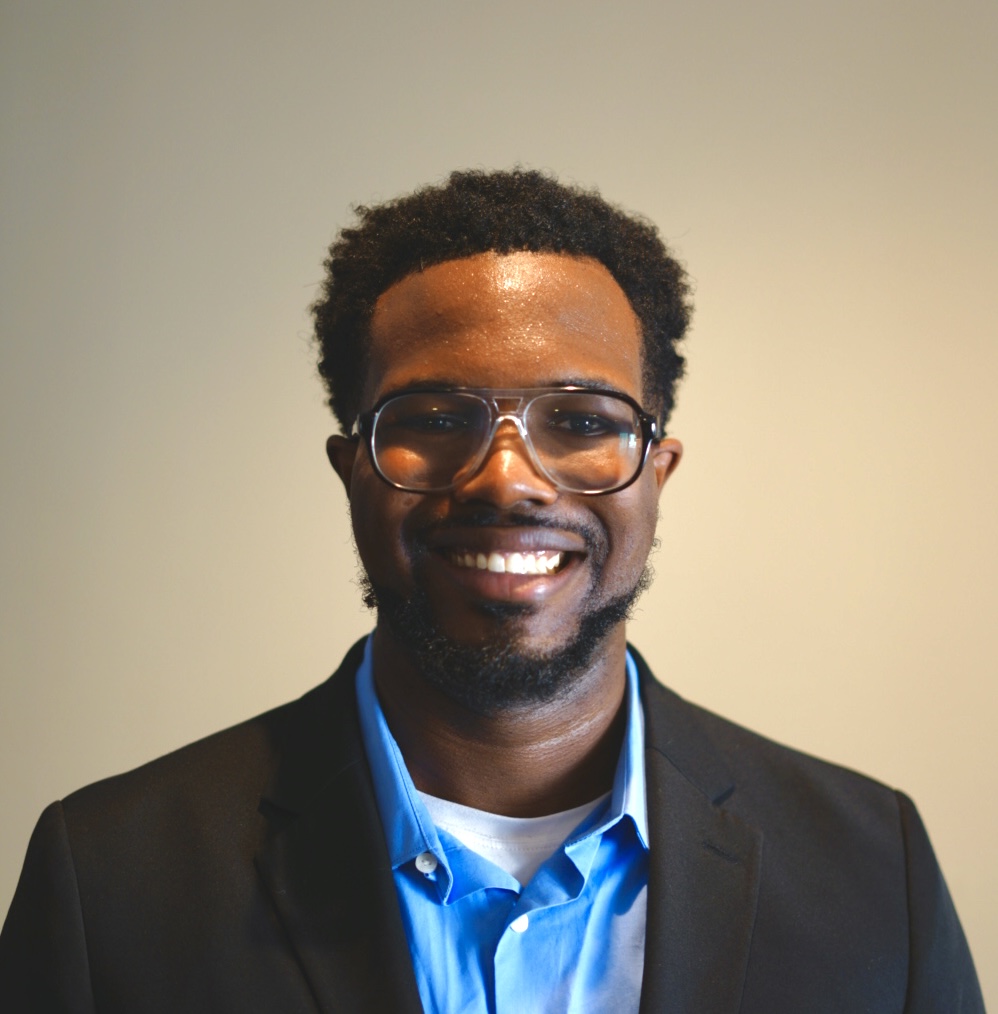
Otuoze Baiye, Founder & Chief Executive
Brooklyn, New York
Registered in SAM. HUBZone and SDVOSB certification support sole source award, set-aside competition, and subcontracting goal credit.
If you are preparing for an examination, navigating a growth event, or reassessing your risk posture, reach out directly.